Eric Labrador
Senior Red Team Operator · Offensive Security
Bio
Eric Labrador is a Senior Red Team Operator with over six years of experience delivering offensive security assurance across the full engagement lifecycle. He specializes in adversary emulation for regulated enterprise and financial sector organizations, conducting Red and Purple Team exercises, physical intrusion assessments, and external and internal penetration testing, including engagements aligned to the compliance requirements of SWIFT network environments.
His assessment scope covers web and API security, Android and iOS application testing, thick client and endpoint reviews, and cloud infrastructure across Azure, AWS, and GCP. He also evaluates Kubernetes cluster security, OT/ICS environments, and AI and LLM-based systems, supported by in-depth source code review across NodeJS, PHP, C#, C++, and Java. Every engagement is delivered with clear, risk-based findings and remediation guidance suited to enterprise governance and audit requirements.
Eric is a recognized contributor to the offensive security community, maintaining open-source tooling published on Burp Suite's BApp Store and publishing original vulnerability research. He holds confirmed findings across multiple HackerOne programs and has presented at The Bug Hunter's Methodology Live alongside Jason Haddix and at DEF CON 34 Las Vegas, where he delivered Certified Re-Pwned: Escalating All the Way Up.
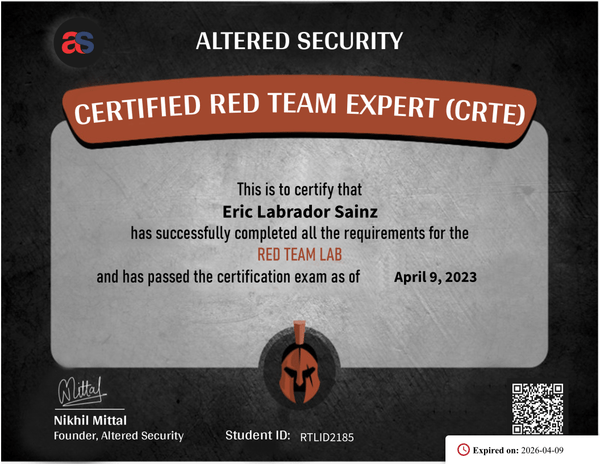
Certifications & Trainings